
Firmware Update and Recovery Mechanisms
Overview
Firmware update and recovery mechanisms ensure that devices can be securely updated, repaired, and restored throughout their lifecycle. Because firmware defines system behavior, attackers frequently target update and recovery paths to:
- inject malicious firmware
- downgrade protections
- corrupt update partitions
- bypass secure boot
- exploit recovery modes
- extract secrets during update routines
A secure update architecture must guarantee:
- authenticity (signed firmware only)
- integrity (hash verification)
- freshness (anti‑rollback)
- atomicity (A/B banks, fail‑safe switching)
- controlled recovery (authenticated fallback paths)
Main Security Threats
Malicious firmware injection
Replacing legitimate firmware with tampered or backdoored images.
Rollback attacks
Forcing installation of older, vulnerable firmware versions.
Insecure update channels
Exploiting unencrypted or unauthenticated paths (UART, CAN, USB, OTA).
Recovery mode abuse
Using boot‑ROM recovery features to bypass authentication or load unauthorized code.
Partial update corruption
Interrupting the update process to leave the system in an inconsistent state.
Key or certificate replacement
Injecting attacker‑controlled signing keys during update.
Supply‑chain manipulation
Compromising firmware before it reaches the device.
Debug interface exploitation
Using JTAG/SWD/UART to force updates or extract firmware.
Side‑channel attacks during update
Extracting keys or signatures from update routines.
Figure 1 — Secure Firmware Update Pipeline with Anti‑Rollback
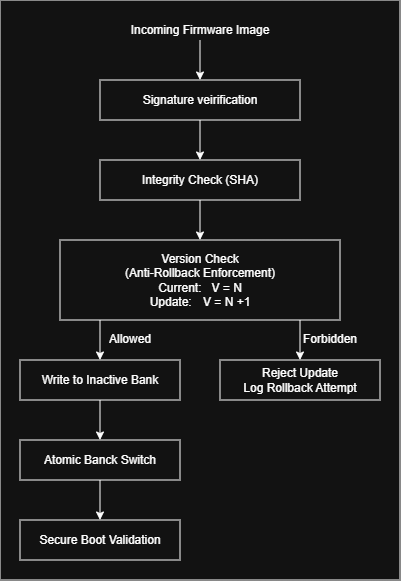
Firmware updates must always move forward. A monotonic version counter prevents installation of older firmware, even if signatures are valid.
Secure Update Mechanisms
Cryptographic signatures
Firmware must be signed using asymmetric keys (RSA, ECC). Verification occurs before installation and again at boot.
Integrity verification
SHA‑based digests ensure the image has not been modified.
Anti‑rollback counters
Monotonic counters or OTP fuses prevent installation of older versions. Even a valid signature cannot bypass rollback protection.
Secure update channels
Encrypted and authenticated transport (TLS, MAC‑protected frames).
Atomic update process
Dual‑bank or A/B partitioning ensures that:
- updates are written to an inactive bank
- the system switches banks only after full verification
- rollback to the previous bank is always possible if validation fails
Update authorization
Only OEM‑authenticated entities can trigger updates.
Rate limiting and DoS protection
Prevents attackers from repeatedly triggering update attempts.
Secure boot integration
Updated firmware is validated at every boot, ensuring persistent trust.
Recovery Mechanisms
Immutable recovery image
A ROM‑based or hardware‑protected fallback image that cannot be modified.
Authenticated recovery mode
Recovery firmware requires cryptographic authorization before execution.
Fail‑safe boot paths
If primary firmware fails validation, the system automatically selects:
- the inactive bank
- or the immutable recovery image
Secure erase
Sensitive data is wiped before entering recovery mode.
Recovery integrity checks
Recovery images must also be signed and hashed.
Controlled debug access
Debug interfaces remain locked or authenticated during recovery.
Figure 2 — Recovery Decision Flow
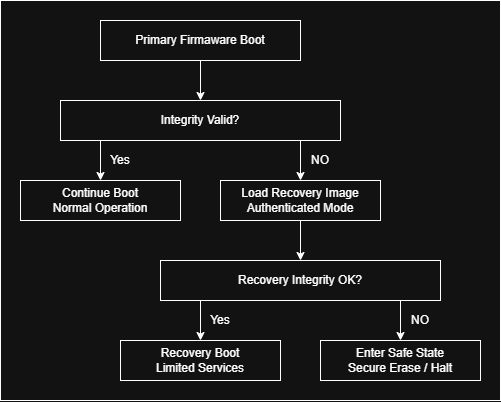
If primary firmware fails validation, the system falls back to a trusted recovery image or enters a safe state.
Relationship with Safety
Safety
Ensures updates do not introduce faults or instability.
Security
Prevents malicious manipulation of the update and recovery process.
Overlap
- Atomic updates prevent both accidental corruption and malicious interruption
- Integrity checks protect against both random errors and tampering
- Recovery mechanisms ensure the system can return to a safe and trusted state
Related Pages
All real, existing pages:
