
FMEDA
Overview
This page provides a detailed view of the FMEDA process, expanding on the concepts introduced in FMEDA Overview.
It explains how failure modes are classified, how diagnostic coverage is calculated, how FIT values are allocated, and how PMHF compliance is verified.
FMEDA is both a quantitative analysis method and a traceability tool, linking architecture, diagnostics, and safety goals.
Figure 1: FMEDA Workflow
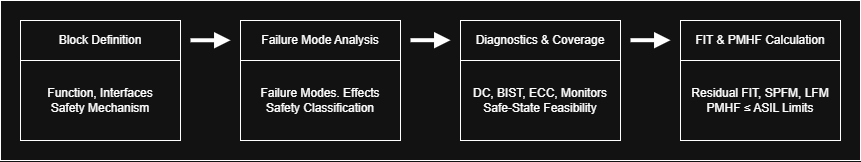
The FMEDA workflow links block definition, failure mode analysis, diagnostic coverage, and quantitative safety metrics. It ensures that each block meets its safety requirements and contributes correctly to system‑level PMHF.
1. Block Definition
Each FMEDA entry begins with a clear definition of the block:
- function
- inputs and outputs
- internal structure (if relevant)
- safety mechanisms
- assumptions of use (AoU)
- operating conditions
This ensures that failure modes and diagnostics are evaluated in the correct context.
2. Failure Mode Identification
Failure modes must be:
- exhaustive
- representative
- consistent with the block’s technology (digital, analog, mixed‑signal)
Typical categories:
Digital Blocks
- stuck‑at faults
- bridging faults
- delay faults
- memory bit flips
- control logic corruption
Analog Blocks
- drift
- saturation
- open/short
- reference instability
- gain/offset errors
Mixed‑Signal Blocks
- ADC/DAC non‑linearity
- sampling errors
- comparator threshold shifts
Each failure mode must be mapped to its effect and safety impact.
3. Failure Effects and Safety Classification
ISO 26262 defines the following categories:
- Safe faults — no safety impact
- Detected faults — detected by diagnostics
- Single‑point faults (SPF) — directly lead to a hazard
- Residual faults — undetected dangerous faults
- Latent faults — hidden faults in redundant paths
- Multiple‑point faults — combinations of faults
Each failure mode must be assigned to one of these categories.
4. Diagnostic Mechanisms
Diagnostics must be listed for each failure mode:
- ECC
- CRC
- watchdogs
- LBIST / MBIST
- analog monitors
- plausibility checks
- redundancy cross‑checks
- timing monitors
- voltage/clock monitors
For each diagnostic:
- coverage
- reaction time
- safe‑state feasibility
- assumptions of use
must be documented.
5. Diagnostic Coverage (DC)
Diagnostic coverage is computed as:
DC determines:
- SPFM
- LFM
- residual FIT
- PMHF contribution
Coverage must be justified with:
- test results
- architectural arguments
- DFT data
- safety mechanism specifications
6. FIT Allocation and Residual FIT
Each failure mode has an associated FIT value:
- intrinsic FIT (from technology)
- derated FIT (based on environment)
- residual FIT (after diagnostics)
Residual FIT is computed as:
Residual FIT contributes directly to PMHF.
7. PMHF Calculation
PMHF is the sum of all residual FIT contributions:
ISO 26262 limits:
- ASIL D → ≤ 10 FIT
- ASIL C → ≤ 100 FIT
- ASIL B → ≤ 300 FIT
FMEDA must demonstrate compliance with these limits.
8. Example FMEDA Table
| Block | Failure Mode | Safety Class | Diagnostic | DC (%) | FIT (dangerous) | FIT (residual) |
|---|---|---|---|---|---|---|
| ADC Front-End | Gain Drift | Latent Fault | Plausibility Cross-Check | 80% | 2.0 FIT | 0.4 FIT |
| SRAM | Bit Flip | SPF | ECC | 99% | 5.0 FIT | 0.05 FIT |
| CPU Core | Control Fault | SPF | Lockstep | 99.5% | 1.0 FIT | 0.005 FIT |
This template can be adapted for digital, analog, and mixed‑signal blocks.
9. Traceability Requirements
FMEDA must be traceable to:
- safety goals
- technical safety requirements
- architecture
- diagnostics
- test results
- assumptions of use
- verification reports
Traceability ensures consistency across the safety lifecycle.
10. FMEDA as a Living Document
FMEDA evolves throughout development:
- updated after architectural changes
- refined after diagnostic implementation
- validated with test results
- finalized for certification
It is not a static spreadsheet — it is a safety engineering tool.
