
ASIL, SEooC, and FIT Metrics in Functional Safety
Overview
Automotive functional safety (ISO 26262) defines a structured approach to evaluating and mitigating risks caused by system malfunctions.
Three foundational concepts guide this process:
- ASIL (Automotive Safety Integrity Level) — the required level of risk reduction for a function
- SEooC (Safety Element out of Context) — a safety‑capable component developed without knowing its final system
- FIT (Failures In Time) — a quantitative measure of hardware failure rates used to verify compliance with ASIL targets
Together, these concepts ensure that safety is measurable, traceable, and consistent across the entire development lifecycle.
Figure 1: Safety Metrics in the ISO 26262 Flow
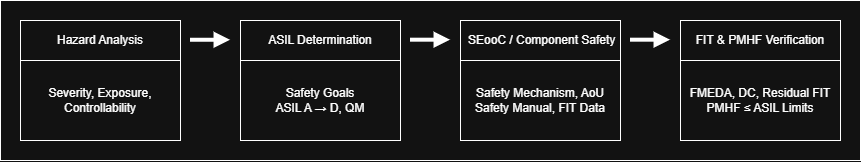
ASIL defines the required safety integrity, SEooC provides reusable safety‑capable components, and FIT metrics verify that the hardware architecture meets the ASIL target. These elements form the backbone of ISO 26262 hardware safety.
ASIL — Automotive Safety Integrity Levels
ASIL defines how critical a function is and how much risk reduction is required.
It is determined during the Hazard Analysis and Risk Assessment (HARA) based on:
- Severity (S) — how harmful the failure is
- Exposure (E) — how often the situation occurs
- Controllability (C) — how easily the driver or system can avoid harm
ASIL levels:
- QM — no safety requirement
- ASIL A — lowest safety integrity
- ASIL B
- ASIL C
- ASIL D — highest safety integrity
Higher ASIL levels require stronger diagnostics, redundancy, architectural constraints, and verification activities.
SEooC — Safety Element out of Context
A SEooC is a component developed without knowing the final system in which it will be used.
Typical SEooCs include:
- MCUs
- PMICs
- sensors
- actuators
- communication controllers
- safety monitors (FCCU, watchdogs)
- software libraries
A SEooC must:
- define assumptions of use (AoU)
- provide safety requirements for the integrator
- implement safety mechanisms and diagnostic coverage
- provide safety documentation (Safety Manual, FMEDA, FIT data)
- meet a target ASIL even without system context
SEooC enables suppliers to build reusable safety‑capable components.
FIT — Failures In Time
FIT is a quantitative measure of hardware reliability:
FIT values are used to:
- estimate random hardware failure rates
- build the FMEDA
- verify compliance with ASIL PMHF limits
- determine required diagnostic coverage and redundancy
FIT contributions come from:
- logic gates
- memories (SRAM, Flash, ECC‑protected blocks)
- analog components
- power stages
- clocking
- interconnects
- external components (PMIC, sensors, actuators)
Relationship Between FIT and ASIL
ASIL levels impose quantitative hardware metrics:
SPFM — Single Point Fault Metric
Measures how well the system avoids single‑point failures.
LFM — Latent Fault Metric
Measures how well the system detects faults that are not immediately visible.
PMHF — Probabilistic Metric for Hardware Failure
Total probability of dangerous hardware failures per hour.
ISO 26262 PMHF limits:
- ASIL D → ≤ 10 FIT
- ASIL C → ≤ 100 FIT
- ASIL B → ≤ 300 FIT
- ASIL A → no PMHF requirement
Implications:
- ASIL D systems must have extremely low dangerous failure rates
- FIT contributions must be summed and evaluated
- diagnostics reduce the dangerous portion of FIT
- architecture must be designed early to meet PMHF limits
Why ASIL and FIT Must Be Considered Early
ASIL classification drives:
- redundancy and architectural patterns
- diagnostic coverage (ECC, CRC, watchdogs, monitors)
- board‑level signaling (fault lines, PMIC integration)
- safe‑state definitions
- component selection
- FMEDA structure and FIT budgeting
If ASIL and FIT are evaluated late:
- PMHF limits may not be met
- diagnostics may be impossible to add
- safe‑state timing may be violated
- certification may fail
- redesign becomes unavoidable
Safety is a top‑down, early‑phase activity.
How ASIL, SEooC, and FIT Work Together
- ASIL defines the required safety integrity
- SEooC provides reusable safety‑capable components
- FIT verifies that the architecture meets the ASIL target
Together, they form the backbone of a compliant safety architecture.
