
DFT for Safety‑Critical Systems
Introduction
DFT techniques must be adapted to satisfy the requirements of functional safety standards such as ISO 26262. Safety‑oriented DFT ensures that faults affecting safety mechanisms, safety‑related functions, and diagnostic features can be detected within the required time constraints.
Why Safety‑Oriented DFT Matters
- Ensures measurable diagnostic coverage
- Supports startup and periodic self‑tests
- Enables safe‑state transitions when faults are detected
- Reduces dangerous FIT contribution
- Provides evidence for safety assessments and audits
Key Topics
Safety‑Oriented LBIST/MBIST
- Startup tests for latent faults
- Periodic in‑field tests
- Partitioning for reduced test time
- X‑tolerance and safe‑state interaction
Diagnostic Coverage Justification
- Mapping faults to safety mechanisms
- Demonstrating coverage for safety‑related blocks
- Handling random‑pattern‑resistant faults
- Complementing LBIST with deterministic ATPG
Test Interval and Detection Latency
- Maximum time a fault may remain undetected
- Impact on Latent Fault Metric (LFM)
- Scheduling periodic tests without violating real‑time constraints
Safe‑State Interaction
- How DFT interacts with system safety mechanisms
- Entering a safe state during test execution
- Avoiding unintended activation of actuators during test
FMEDA Integration
- Linking DFT results to FMEDA tables
- Diagnostic coverage contribution
- Residual fault analysis
- FIT allocation and justification
Diagrams, examples
Figure 1: Periodic LBIST

Periodic in‑field LBIST detects latent faults that may accumulate during system operation. The system enters a safe state, runs the LBIST sequence, and returns to service if no fault is found. When a fault is detected, diagnostic coverage and FMEDA data are updated, and the system triggers the appropriate safe reaction according to the safety concept.
Figure 2: Diagnostic coverage

Diagnostic coverage quantifies the effectiveness of a safety mechanism in detecting faults within a safety‑related block. The fault space is evaluated by LBIST, MBIST, monitors, or ATPG, producing detected, undetected, and not‑covered faults. Diagnostic coverage is computed as the ratio of detected faults to the total detectable faults, and the result feeds directly into the FMEDA to determine residual faults and FIT allocation.
Figure 3: DFT ↔ FMEDA relationship
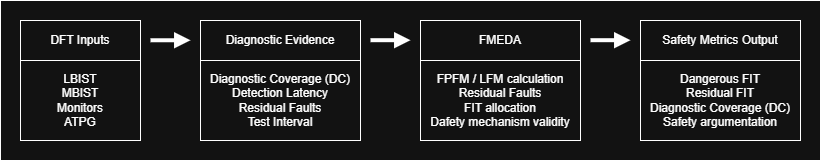
DFT mechanisms such as LBIST, MBIST, ATPG, and monitors provide the diagnostic evidence required by the FMEDA. This includes diagnostic coverage, detection latency, residual faults, and test interval. The FMEDA uses this information to compute safety metrics such as SPFM, LFM, and FIT allocation, forming the basis for the safety argumentation of the system.
