
Data Integrity — Hardware Perspective
Overview
Data integrity is a fundamental security property ensuring that data is not modified, corrupted, or forged as it moves through a system. While integrity can be enforced at multiple layers (protocol, software, cryptographic), in a modern SoC the strongest guarantees come from hardware.
This page focuses on how integrity is implemented and enforced in hardware, across:
- datapath pipelines
- internal buses
- DMA engines
- memory subsystems
- packet processors
- cryptographic accelerators
- HSM‑controlled key hierarchies
This is the architectural counterpart to the conceptual page Data Integrity — Overview.
Integrity in the Data Path
In high‑speed datapaths, integrity must be enforced inline, at line‑rate, with deterministic latency.
Hardware mechanisms include:
- GCM / GMAC authentication tags
- HMAC for non‑AEAD protocols
- CRC + MAC combinations
- Authenticated headers
- Replay counters
- Integrity metadata propagation
Why hardware?
- The CPU cannot authenticate every packet at 10G/25G/100G
- Integrity checks must be performed before data enters trusted buffers
- Latency must be deterministic
- Attackers may inject corrupted data at PHY, MAC, or bus level
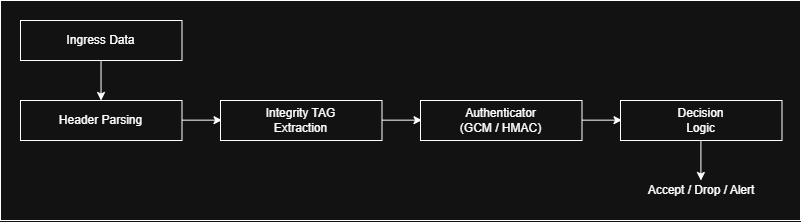
Typical datapath integrity pipeline
Integrity in Internal Buses
Internal SoC buses (AXI, AHB, TileLink, CHI) are vulnerable to:
- malicious bus masters
- compromised DMA engines
- corrupted transactions
- replayed transactions
- address spoofing
Hardware integrity mechanisms include:
- Transaction tagging (ID, domain, privilege)
- Bus firewalls
- Address range enforcement
- Per‑transaction integrity metadata
- Replay protection for coherent fabrics
- End‑to‑end integrity from master to memory
Example: AXI Integrity Flow
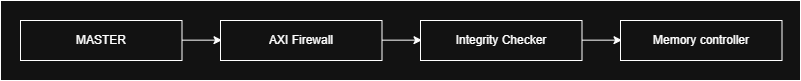
The firewall enforces who can access what. The integrity checker enforces whether the data is valid.
Integrity in DMA and Memory Subsystems
DMA engines are a major attack surface because they can:
- bypass the CPU
- write directly into memory
- corrupt buffers
- inject forged packets
Hardware integrity protections include:
- IOMMU (address translation + access control)
- DMA integrity tags
- Memory poisoning detection
- ECC (Error‑Correcting Code)
- Authenticated memory regions
- Per‑buffer integrity metadata
ECC vs Cryptographic Integrity
| Mechanism | Purpose | Strength |
|---|---|---|
| ECC | Detects random bit flips | Not secure against attackers |
| CRC | Detects accidental corruption | Not secure against attackers |
| MAC / GCM | Detects intentional tampering | Cryptographically strong |
ECC and CRC protect against noise. MAC/GCM protect against attackers.
Integrity in Packet Processing Pipelines
Packet processors (parsers, classifiers, schedulers) must validate integrity before packets enter trusted queues.
Hardware checks include:
- header integrity
- length consistency
- authenticated tags
- sequence counters
- freshness windows
- cross‑layer integrity (L2+L3+L4)
Example pipeline

If integrity fails, the packet is dropped before classification.
Interaction with the HSM
The HSM is responsible for:
- deriving integrity keys
- wrapping/unwrapping keys
- enforcing key usage policies
- injecting keys into accelerators
- isolating key material from the CPU
Integrity key flow
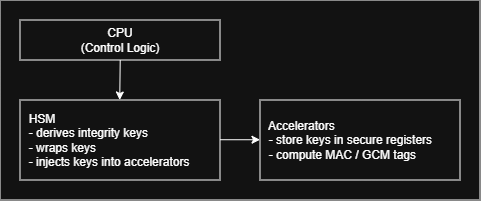
Keys never appear in plaintext outside secure hardware.
Integrity Metadata Propagation
Modern SoCs propagate integrity metadata alongside data:
- validity bits
- authentication tags
- domain identifiers
- privilege levels
- freshness counters
This metadata travels through:
- buffers
- FIFOs
- pipelines
- bus transactions
- DMA descriptors
ensuring that integrity is preserved end‑to‑end.
Threats and Mitigations
| Threat | Hardware Mitigation |
|---|---|
| Data tampering | GCM/HMAC authentication |
| Replay attacks | Sequence counters + replay window |
| Bus injection | Bus firewalls + transaction tagging |
| DMA corruption | IOMMU + authenticated DMA |
| Memory corruption | ECC + authenticated memory |
| Forged packets | Inline integrity verification |
| Compromised CPU | HSM‑enforced key usage policies |
